


AI SOAR v3.0 の動作を見る
Deep AI Agent Testing の動作を見る
OT, UAS, and autonomous systems
Secure the systems that move, control, and sustain the mission
AI SOAR extends agentic security operations into industrial environments, public-safety fleets, and contested or disconnected UAS missions. Evidence is scoped to the customer profile, retained for audit, and linked to findings, remediation, and retesting.
Operational technology security
Inventory PLCs, RTUs, HMIs, robotics, medical devices, and industrial networks; monitor protocol and configuration drift; and map evidence to NIST SP 800-82, NIST SP 800-53, IEC 62443, CMMC, and sector controls.
Drone and UAS assurance
Assess firmware, flight controllers, C2 links, AI autonomy, GPS resilience, RF observations, Remote ID, supply-chain provenance, and mission safety with profile-scoped evidence and human approval gates.
AI エージェント攻撃への備え
この評価は二層をテストします。ZeroTrusted.ai の AI Firewall はプロンプト、ツール、データにポリシーを適用し、AI SOAR は相関、調査、対応を行います。20 の Agent Escape シナリオが、エージェントを指示、ツール、権限の外へ押し出します。
プラットフォーム モジュール
バージョン 3.0 は、セキュリティ ライフサイクル全体にわたる 6 つの統合モジュール グループで、エンドツーエンドのセキュリティ オーケストレーションを提供します。
コマンド センター
すべてのセキュリティ運用にわたる統合された状況認識。SOAR ダッシュボード、モジュール間リスク統合、12 以上のソース タイプを集約する統合検出パイプライン、STIX/TAXII を備えた脅威インテリジェンス、および MTTD/MTTC/MTTR KPI を備えた継続的な監視。
オーケストレーション
FIPS 199 分類によるシステム セキュリティ プロファイル、SCAP 互換性を備えた資産インベントリ管理、ゼロトラスト継続認証による認可境界、および NIST SP 800-161 による SBOM 追跡を備えたサプライ チェーン リスク評価。
自動化
SSP/SAR/POA&M 用の AI ドキュメント ジェネレーター、SAST および DAST スキャン、ネットワーク スキャン、DISA STIG チェッカー、パケット キャプチャ、AI ポリシー生成ウィザード、パッチ管理、およびイベント駆動プレイブックを備えたワークフロー自動化エンジン。
レスポンス
NIST SP 800-61 に基づくエンドツーエンドのインシデント対応、スキャン結果から自動生成する POA&M トラッカー、SHA-256 保管連鎖を備えたフォレンジック証拠収集、CP/IR 計画テスト、チーム セキュリティ評価、およびログ アーティファクト管理。
AI CNO プラットフォーム
Counter-AI および情報作戦のための 12 の専門エージェント。Red AI probing、シグナル インジェクション、MCP インターセプト、モデル抽出、敵対的テスト、戦闘被害評価、ナラティブ戦、合成メディア分析、および影響ネットワーク マッピング。
自律型 SOC
AI SOAR は、ユーザー、ワークロード、インフラストラクチャに応じてシームレスに拡張します。コンピュート、GPU リソース、メモリ、ストレージを追加すると、プラットフォームはそれらのリソースを自動的に活用してスループットを向上させ、AI 推論を高速化し、より多くの同時トランザクションを処理し、応答時間を短縮します。これにより、組織は小規模な導入からエンタープライズ規模の環境へと成長しながら、高いパフォーマンス、耐障害性、信頼性を維持できます。
AI SOAR module catalog
One platform for the complete security, privacy, GRC, and agent lifecycle.
The navigation changes as new tools and agents ship. The module groups below describe the operating model while the live installation remains the source of truth for enabled features, versions, permissions, and runtime readiness.
無料のトレーニング動画は、稼働中の AI SOAR プラットフォームで収録しています。AI で編集し、AI ナレーション付き。 AI SOAR トレーニングシリーズを見る
Command Center
Executive situational awareness and cross-module risk decisions.
Dashboard · Command Center · Enterprise Scale · Launchpad · Risk Management · Unified Findings · Threat Intelligence · Test Scheduler · Continuous Monitoring
Dashboard
Command Center
Enterprise Scale
Launchpad
Unified Findings
Asset Management
Maintain the profile, asset, boundary, facility, supplier, and architecture context needed for defensible assessments.
Profiles · Inventory · Discovery · Supply Chain Risk · MSSP Dashboard · Customer Operations · Enterprise Operations Catalog · Edge Endpoints · Boundaries · Interconnections & ISAs · Architecture Diagrams
Profiles
Inventory
Discovery
Customer Operations
Enterprise Operations Catalog
Boundaries
Architecture Diagrams
Security Testing Command Center
Run authorized security testing and preserve the target, authorization, tool, evidence, and remediation chain.
Testing Hub · Mission Chain · Pen & Assessments · Prompt Workbench · Wireless / RF Security · Code Analysis · DAST · AI AppSec Assessment · Network Intelligence · PCAP Reader · ZTA Validator
Testing Hub
Prompt Workbench
Threat Response
Move a verified finding through containment, remediation, recovery, and retest.
Incident Response · POA&M · CP/IR Testing · Patch Management · Forensics
Incident Response
POA&M
AI Agents
Register, authorize, teach, version, and coordinate agents with explicit skills, tools, models, and autonomy limits.
Agent Hub · SWARM · Workforce · Agent Tools
Agent Hub
SWARM
Workforce
Agent Tools
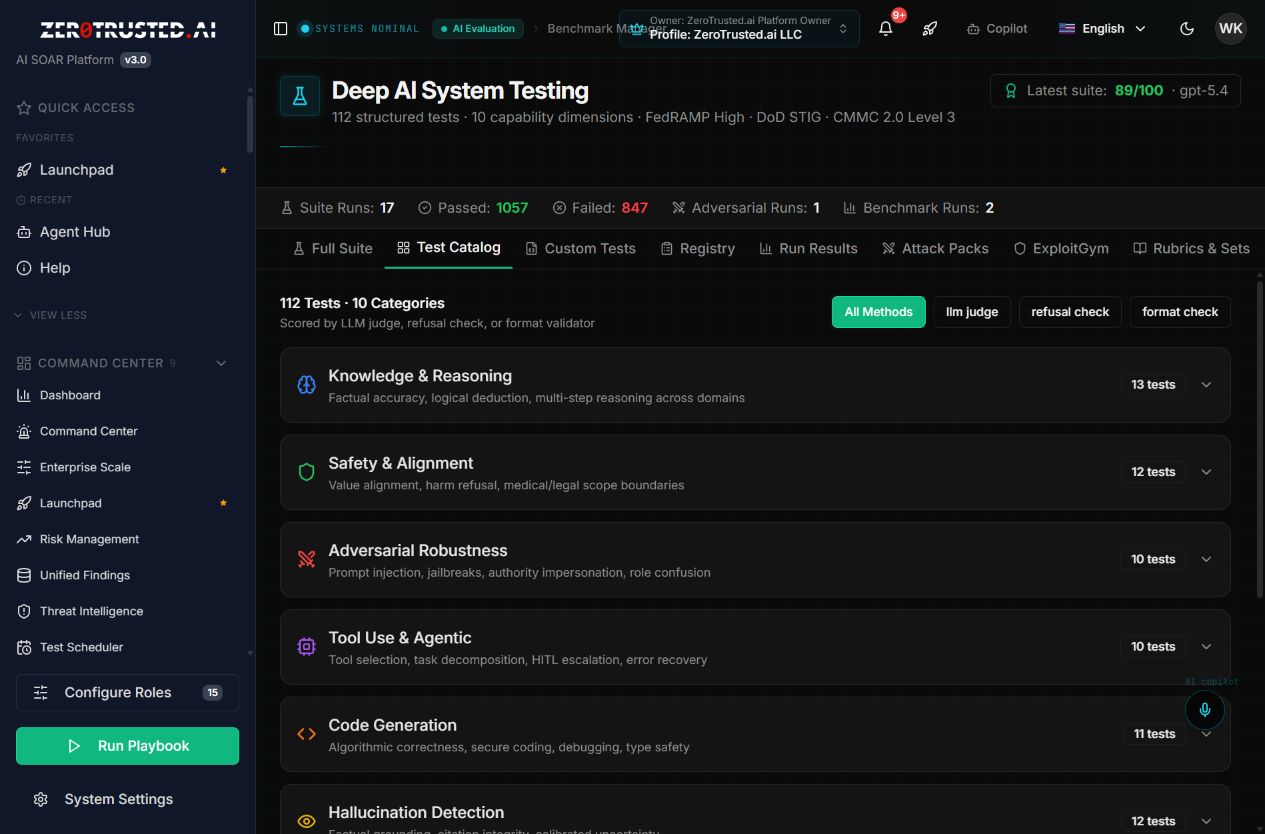
Deep AI System Testing
Prove that agents are safe, useful, traceable, and ready before release or after a skill or model change.
Benchmark Manager · Human Review Workbench · Agent Mission Trace · Adversarial Testing · Agent Verification · SWARM Routing Ledger · Agent Remediation Hub · Agent Preflight Ops · Evidence Package Export · OpenClaw · AI-Infra-Guard
Benchmark Manager
Human Review Workbench
Agent Mission Trace
Adversarial Testing
Agent Verification
SWARM Routing Ledger
Agent Remediation Hub
Agent Preflight Ops
Evidence Package Export
OpenClaw
AI-Infra-Guard
AI Operations
Control model usage, runtime guardrails, costs, infrastructure, AI assets, and security assurance.
AI Observability · Semantic Grounding · AI Guardrails · AI WAF · AI Firewall · AI HealthCheck · AI Governance · AI Asset Inventory · AI Security Assessment · DRM Usage · Automation · K8s Security · NVIDIA Platforms
AI Observability
Semantic Grounding
AI Guardrails
AI WAF
AI Firewall
AI HealthCheck
AI Governance
AI Asset Inventory
AI Security Assessment
DRM Usage
Automation
K8s Security
NVIDIA Platforms
Autonomous SOC
Correlate SIEM, EDR, identity, email, cloud, and communications telemetry into governed response workflows.
Module Setup & Prerequisites · Autonomous SOC · SIEM & Logs Hub · EDR Hub · ITDR · Email Security · Human Interaction Threats · Cloud Security · SOC Comms · Digital Twin
Module Setup & Prerequisites
Human Interaction Threats
Cloud Security
SOC Comms
Digital Twin
Attack Surface
Find exposure, weak signals, deception opportunities, and detection engineering gaps before an attacker does.
UEBA · Detection Rules · Detection Engineering · Attack Surface · Deception · OSS Security Stack
Detection Rules
Detection Engineering
Deception
OSS Security Stack
Automation and Compliance
Turn controls, evidence, documents, and sector requirements into repeatable customer workflows and exports.
Doc Generator · AI Policy Wizard · Document Library · Generated Docs · Reports · Controls · Evidence · Personnel & Roles · Policies · SCAP Content · Sector Compliance
Doc Generator
AI Policy Wizard
Reports
Controls
Personnel & Roles
Policies
Sector Compliance
Sector Compliance
Start with a sector profile and map tests, tools, evidence, owners, and reporting to the customer’s requirements.
Banking & Financial · Health (HIPAA) · Government (FISMA) · CMMC 2.0 · Energy (NERC CIP) · Insurance · SOC 2 Type II · ISO 42001 AI Mgmt · EU AI Compliance · Japan AI Compliance · Brazil AI Compliance · Fraud Detection · AML/KYC Center
Banking & Financial
Health (HIPAA)
Government (FISMA)
CMMC 2.0
Energy (NERC CIP)
SOC 2 Type II
ISO 42001 AI Mgmt
EU AI Compliance
Japan AI Compliance
Brazil AI Compliance
Fraud Detection
AML/KYC Center
OT, mission, and administration
Extend the same evidence and identity model into physical operations, autonomous systems, and platform administration.
OT Security · Manufacturing · Robotics · Medical Devices · ICS Controllers · Military & Drone Security · AI CNO Platform · CNO Operations Console · Configure Roles · Customer Portal · Connections · Deployment Guide · Help
Configure Roles
Customer Portal
AI セキュリティ レイヤー
ファイアウォール、ヘルス検証、アプリケーション セキュリティ評価、ガードレール、Web アプリケーション ファイアウォールを含む多層 AI 保護。
Deep AI System Testing
Authorizing Officer (AO) 提出のための構造化された敵対的テストと証拠パッケージングを備えた包括的な AI 評価フレームワーク。
エージェント ミッション トレース
リアルタイム WebSocket ストリーミングを備えたツール コール、承認イベント、メモリ参照、実行タイミングのエンドツーエンド タイムライン。
証拠パッケージのエクスポート
SHA-256 ハッシュ チェーン、OpenEval-v1.2 スキーマ検証、改ざん防止署名を備えたワンクリック バンドル。
分類バナー
機密展開環境向けに、非機密および CUI から国家安全保障上の最高の分類レベルまでのバナー。
脅威検出スイート
14 のコンプライアンス フレームワーク
政府、ヘルスケア、金融、エネルギー部門向けの事前構築された管理マッピング、自動化された証拠収集、およびセクター固有のコンプライアンス。
インフラストラクチャと展開
自動インストール、セキュリティ強化、ゼロトラスト ID 管理を備えたオンプレミスまたは主要クラウドへの展開。