

Secure Operational AI
Easily build secure agents and tools for any mission.
ZeroTrusted.ai . . . The AI/SI Force Multiplier for your enterprise, department, and/or projects/programs
ZeroTrusted.ai enables secure operational AI and AI agents, no matter the mission. Bring your own AI, and we add a security, privacy, and transparency layer over it and over the systems you already run, from the tactical edge to the enterprise, with no rip-and-replace.
Build secure agents and tools in six simple steps
No new stack. No new model. No code changes to the systems you already run.
- 1
Bring your AI.
Commercial LLMs with your own keys, or self-hosted and local models. Assign an approved model to each agent.
- 2
Connect your systems.
SIEM, EDR, identity, email, cloud, ticketing, threat-intelligence, and OT connectors, or your own.
- 3
Build or clone an agent.
Start from a shipped agent or register your own. Give it an identity, an owner, skills, tools, and a mission.
- 4
Set the guardrails.
Permissions, tool allow-lists, autonomy limits, and approval policy, with AI Firewall policy on every prompt, response, and tool call.
- 5
Test before you trust.
One-button preflight, benchmarks, adversarial and escape testing, and human review, ending in a signed evidence package.
- 6
Put it to work.
High-impact actions wait for a person, every action is traced, and findings drive remediation and retest.
Works the same on a forward-deployed laptop and in the enterprise data center.
The problem is trust, not technology
AI is ready to do real mission work. Most missions are not yet allowed to use it. Security teams need to know who sees the data, what an agent is allowed to do, and whether anyone can prove what happened. Without those answers, the safe decision is "no," and AI stays in the demo.
At the same time, cleared and certified experts are the hardest people to staff, and AI agents bring a new kind of insider risk: valid credentials do not equal unlimited authority.
A secure layer over what you already run
Secure the AI you already use
The AI Firewall and AI Gateway inspect every prompt, response, and tool call, whether the model is ChatGPT, Claude, Gemini, a self-hosted LLM, or an internal agent framework. Bring your own keys and keep control of your providers.
Connect the tools you already own
AI SOAR connects to your SIEM, EDR, identity, email, cloud, ticketing, threat-intelligence, and OT tools, and adds governed AI agents that test, investigate, explain, remediate, and retest with evidence.
Build secure agents, tools, and operations
Register your own agents, clone and adapt existing ones, and add your own tools and connectors. Every agent passes preflight and testing before it touches a mission and stays inside its permissions and autonomy limits.
Bring Your Own AI (BYOAI)
Bring your own AI. We make it secure, governed, and transparent.
Keep the commercial LLMs you have contracted, the open-source models your engineers run, the agents your teams built, and the tools and MCP servers they call. ZeroTrusted.ai secures, governs, and makes them transparent without changing them.
You bring
Commercial LLMs
such as ChatGPT, Claude, and Gemini, with your own keys
ZeroTrusted.ai adds
Inspection of every prompt and response, DLP and redaction, policy routing, and audit. You keep the provider relationship, billing, and data routing.
You bring
Open-source and local models
through Ollama, vLLM, LM Studio, llama.cpp, or NVIDIA NIM
ZeroTrusted.ai adds
No-egress operation, hardware-fit guidance, and a curated catalog that shows each model's country of origin and supply-chain risk.
You bring
In-house agents and agent frameworks
ZeroTrusted.ai adds
Agent identity, owner, permissions, and autonomy limits; preflight and adversarial testing; and a full mission trace.
You bring
Tools, MCP servers, and plugins
ZeroTrusted.ai adds
Tool allow-lists, argument inspection, revocation on a policy violation, and supply-chain integrity checks.
Inline, out-of-band, or browser-edge enforcement; HealthCheck runs alongside your models with no code changes to the application. Switch models and your policies, approvals, and evidence stay the same.
One secure layer, from the tactical edge to the enterprise.
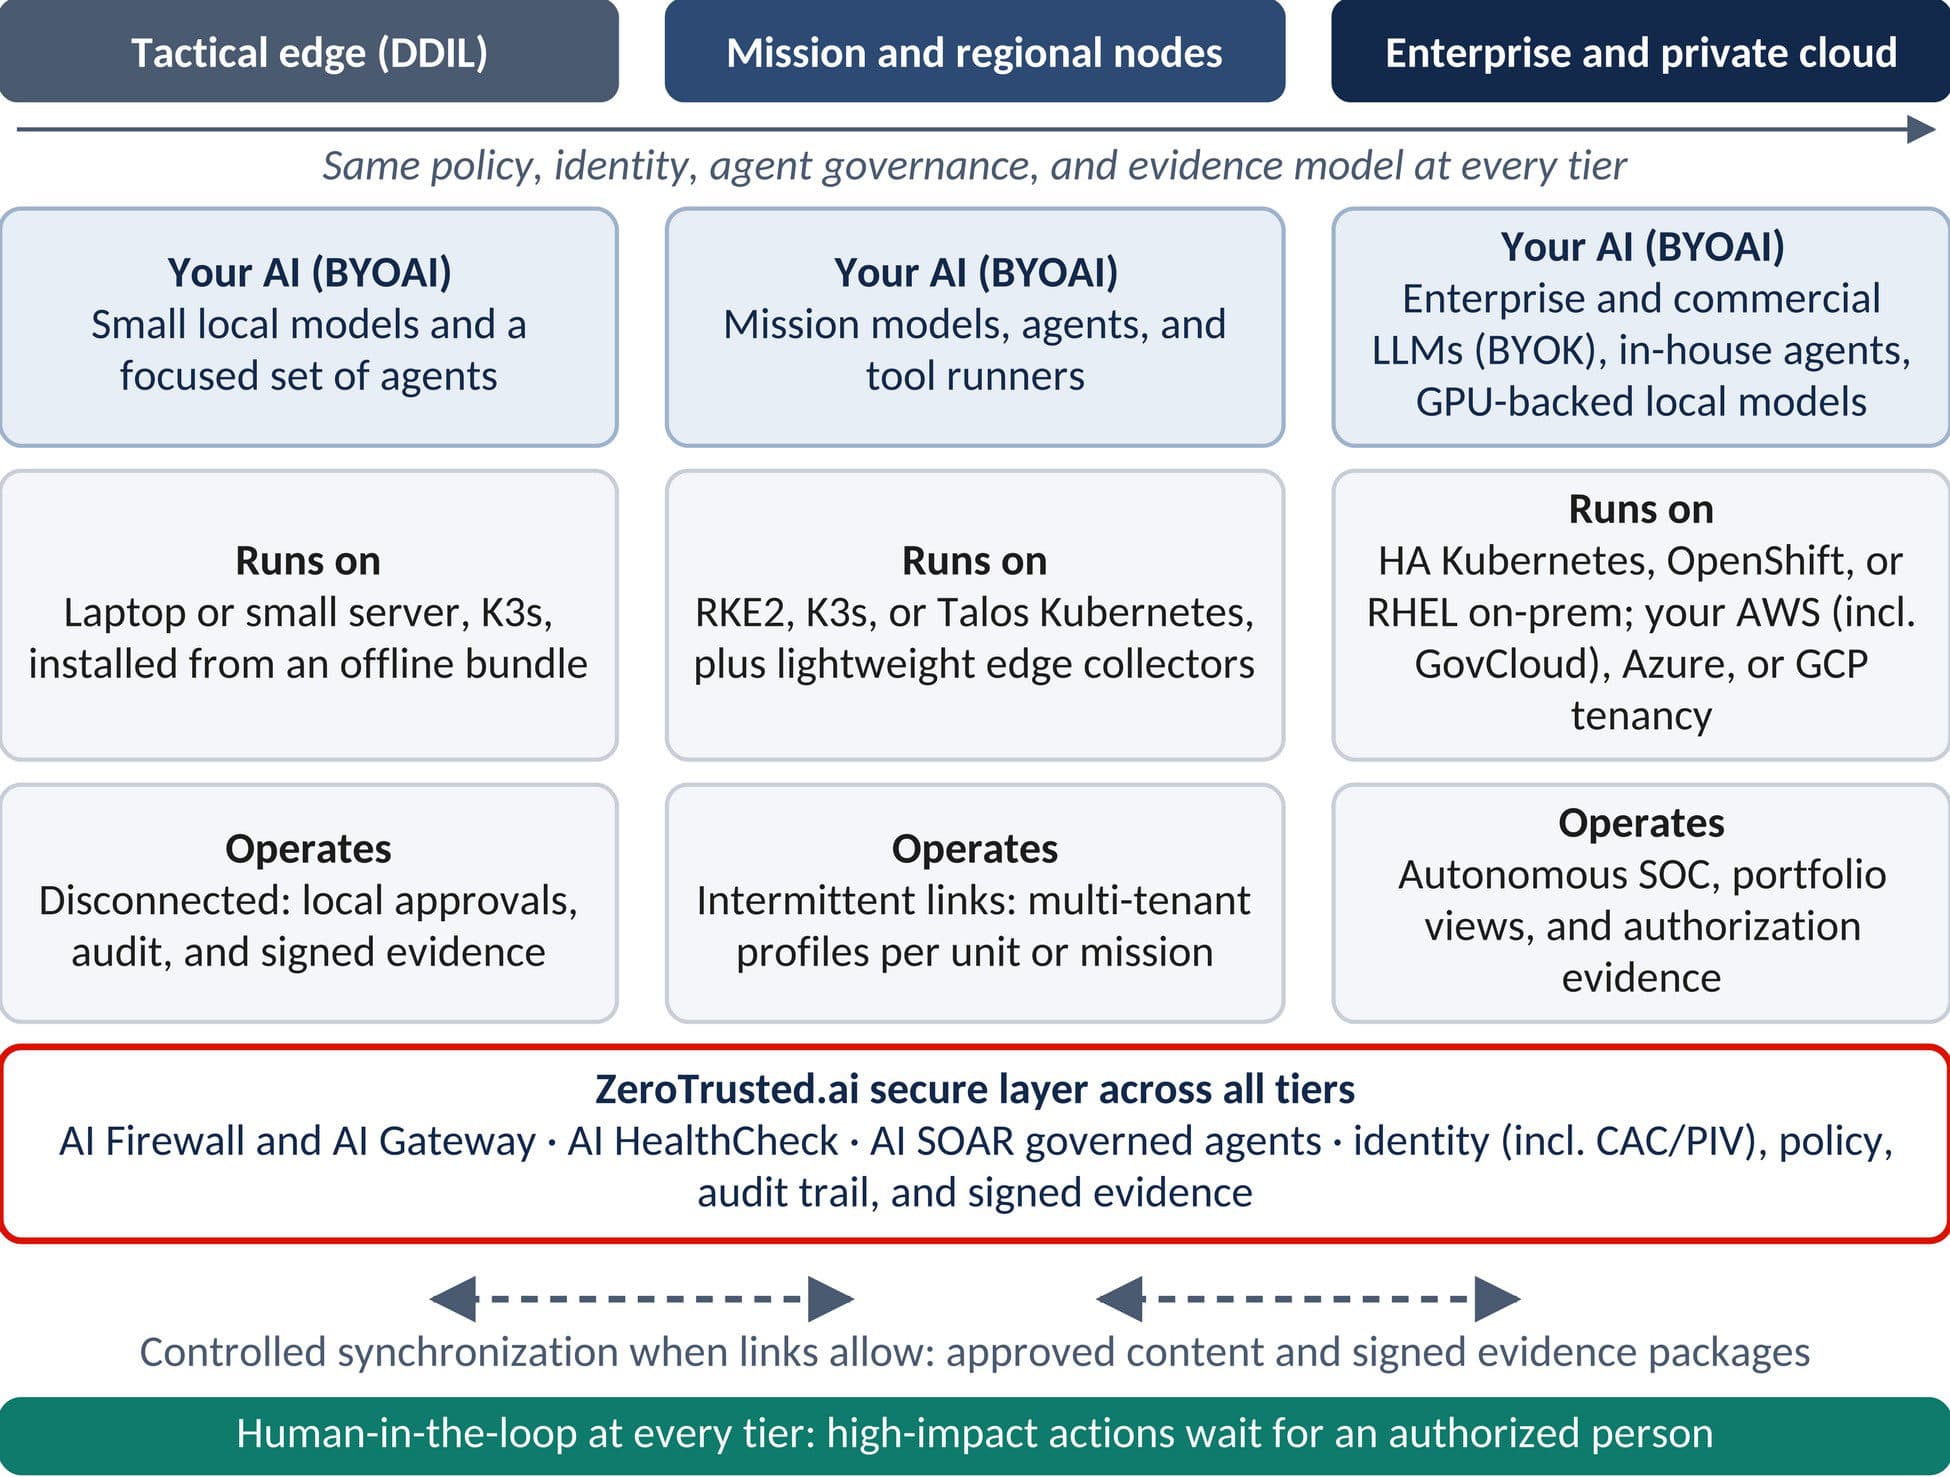
Missions don't happen only in the data center. ZeroTrusted.ai uses the same policy, identity, agent governance, and evidence model at every tier, and it scales from a small laptop to a large enterprise cluster.
Tactical and disconnected edge (DDIL)
A small-footprint install from an offline bundle, with local models, a focused set of agents, and local approvals, audit, and signed evidence. No reach-back required.
Mission and regional nodes
Hardened Kubernetes (RKE2, K3s, Talos) for mission agents, models, and tool runners, with lightweight edge collectors and multi-tenant profiles per unit or mission.
Enterprise and private cloud
HA Kubernetes, Red Hat OpenShift, or RHEL on-premises, or your own AWS (including GovCloud), Azure, or Google Cloud tenancy, with GPU capacity, the Autonomous SOC, and portfolio views.
Across every tier
Controlled synchronization moves approved content and signed evidence packages when links allow, and high-impact actions always wait for an authorized person.
How a secure agent goes to work
- 1
Register
- 2
Preflight
- 3
Test
- 4
Review and certify
- 5
Operate
- 6
Remediate and retest
Every agent gets an identity, an owner, an Agent-BOM, and autonomy limits. Humans review results before an agent is fielded, high-impact actions wait for approval, and missing tools stay visible instead of being faked.
A force multiplier for cleared and certified workforces
More missions per operator. People stay in charge.
Cleared SMEs are hard to find. Our secure agents take on repeatable analysis, triage, evidence collection, and documentation, so your cleared and certified people can focus on judgment, decisions, and execution. Agents augment people; they do not replace them. Every consequential action stays human-in-the-loop.
For mission owners
Execute more operations, faster and more consistently, within existing accredited boundaries.
For primes and integrators
Deliver secure AI agents inside your own service delivery and make every cleared team member more effective.
For CISOs
See which work roles are covered by people, by governed agents, or by neither.
Security. Privacy. Transparency. Every time you go to work.
Security
Zero Trust for users, models, and agents. Prompt-injection and jailbreak blocking, tool allow-lists, Agent Escape testing, and CAC/PIV, SAML, OIDC, and LDAP sign-in.
Privacy
PII, PHI, secrets, classified markings, and custom sensitive terms are redacted or blocked before a prompt leaves your perimeter. With local models, nothing needs to leave the network.
Transparency
Every prompt, response, tool call, and approval is logged. Agent Mission Trace shows what each agent did, and evidence packages are hash-chained and tamper-evident. Missing evidence is never treated as a pass.
Framework mappings (for example NIST SP 800-53, NIST AI RMF, and OWASP agentic risks) help organize evidence. They do not establish certification or compliance; your assessor or authorizing official decides.
Built for any mission
Cyber operations and SOC
Governed investigation and response with human approval for high-impact actions. Your team runs its own operations.
Insider threat and UAM
Evidence-readiness assessments for User Activity Monitoring, Human Insider Threat, and AI Agent Insider Threat. Not a surveillance sensor; people make the decisions.
Supply chain risk
SBOM tracking, Agent-BOMs, and model-integrity checks for models, tools, MCP servers, and plugins.
OT, UAS, and disconnected missions
OT and drone assurance, evidence-only by default, with air-gapped installs and local models.
Enterprise IT and AI adoption
Govern public AI use with the AI Firewall and Shadow AI Protection, and put agents to work inside existing service-desk workflows.
Illustrative workflows, not customer case studies.
Deploy where the mission runs
ZeroTrusted.ai is enterprise software that you install and operate inside your environment and authorization boundary: forward-deployed and DDIL nodes, on-premises, private cloud, your own AWS (including GovCloud), Azure, or Google Cloud tenancy, Red Hat OpenShift, or isolated and air-gapped networks with local models. You keep your data, models, keys, and policies.
Start with one mission
- 1
Start a free trial.
15 days online, no credit card required.
- 2
See it on your workflows.
Request a demonstration.
- 3
Run a scoped pilot
In your environment, measured on your own operations.
- 4
Buy through CDAO Tradewinds (Awardable)
Or through your prime contractor.
White paper
Secure Operational AI: Enabling AI and AI Agents for Any Mission
ZeroTrusted.ai . . . The AI/SI Force Multiplier for your enterprise, department, and/or projects/programs. How to put AI and AI agents to work on real missions without changing the systems and AI you already use. Covers Bring Your Own AI, the edge-to-enterprise architecture, the secure agent lifecycle, the force-multiplier model for cleared workforces, mission use cases, and deployment options.